Ubuntu in 2026: From Rust-Powered Core Utils to Raspberry Pi Livepatch
Ubuntu in 2026: From Rust-Powered Core Utils to Raspberry Pi Livepatch
Ubuntu's 2026 lineup is the most consequential in years. The 11th long-term support release rewrites the security floor with Rust, the Raspberry Pi gets live kernel patching for the first time, and WSL gains a full container runtime that doesn't need Docker. Here's the complete picture.
Ubuntu 26.04 LTS: Resolute Raccoon
Released April 23, 2026, Resolute Raccoon is supported until at least 2031 -- or 2038 with Ubuntu Pro and the Legacy add-on[1]. It ships Linux kernel 7.0, GNOME 50, and a stack of changes that affect every layer of the system.
The kernel
Linux 7.0 is the foundation. Notable changes:
- Rust is no longer experimental in the kernel. The upstream experiment flag is gone; Rust is now a permanent part of the kernel build system[2].
- PREEMPT_RT is mainline. The real-time kernel is available in the main archive for the first time outside Ubuntu Pro[2].
- Livepatch now covers ARM64, not just x86_64. Canonical and the upstream community spent two years building the toolchain prerequisites -- reliable stack trace checks and the consistency model -- needed to hot-swap code on ARM processors[3].
- ZFS 2.4.1 and DOCA-OFED 26.01 kernel modules ship out of the box[2].
GNOME 50 and the Wayland shift
The X11 GNOME session is gone. Ubuntu 26.04 is Wayland-only[4].
What GNOME 50 brings:
| Feature | Detail |
|---|---|
| Fractional scaling | Enabled by default; optimized to minimize blur |
| VRR | Variable refresh rate no longer experimental |
| HDR | Record and screen-share HDR content natively |
| New default apps | Ptyxis terminal, Resources system monitor (written in Rust), Papers PDF viewer, Loupe image viewer, Showtime video player |
| Reduced Motion | New accessibility toggle to suppress animations |
| Remote desktop | Hardware-accelerated, HiDPI-correct, webcam passthrough |
| Sysprof | Installed by default for performance profiling |
The Rust oxidation
This is the headline story for system administrators. Ubuntu 26.04 replaces two foundational components with memory-safe Rust rewrites[5]:
sudo-rs replaces the classic sudo binary. It's a complete rewrite that eliminates the class of bugs that produced Baron Samedit (CVE-2021-3156) and similar privilege-escalation CVEs. The command syntax is unchanged. One visible difference: password feedback is now enabled by default (asterisks appear while typing). The original sudo is available as sudo-ws if needed.
rust-coreutils replaces the GNU core utilities (ls, cp, mv, cat, base64, etc.) with the uutils Rust implementation. The GNU versions remain accessible with a gnu prefix -- run gnuls for the classic ls. Canonical reports measurable performance improvements, particularly in base64.
Security highlights
- TPM-backed full disk encryption graduates from experimental to production-ready. The drive can only be decrypted by the hardware it was installed on, with Secure Boot enabled[5].
- Post-quantum cryptography: OpenSSH and OpenSSL use post-quantum algorithms by default[6].
- Web servers reject legacy TLS out of the box[5].
- Identity services refuse to run as root[5].
- Confidential computing: full host and guest support for AMD SEV-SNP and Intel TDX[7].
AI and GPU compute
NVIDIA CUDA and AMD ROCm are available directly from the official repositories for the first time in an LTS[4]. Combined with MAAS's new NPU auto-detection for bare-metal provisioning, Ubuntu 26.04 positions itself as the default platform for AI workloads.
Server and infrastructure
- LXD hosts both system containers and VMs from a single daemon.
- Virtualization HWE stack: QEMU, libvirt, OVMF, and SeaBIOS now follow a rolling enablement window inside the LTS lifecycle, upgraded every six months for the first two years[7].
- Netplan continues as the default network stack with improved AD integration, cloud auth against EntraID/Google, and NTS secure time sync[8].
- IgH EtherCAT Master is integrated into the kernel for industrial real-time networking[4].
Ubuntu on Raspberry Pi
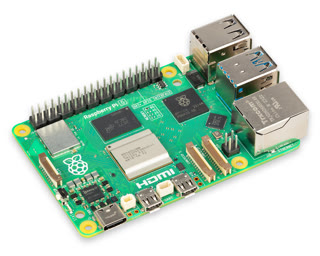
The Pi story in 2026 has two parts: broader board support and a historic security upgrade.
Board support matrix (26.04 LTS)
| Board | Server | Desktop | Compute Module |
|---|---|---|---|
| Pi 3B/3B+/3A+ | Yes | -- | -- |
| Pi 4B | Yes | Yes | CM4: Yes |
| Pi 400 | Yes | Yes | -- |
| Pi 5 | Yes | Yes | -- |
| Pi 500 | Yes | Yes | -- |
| Zero 2W | Yes | -- | -- |
Desktop images now ship as a dedicated ARM64 ISO -- no longer just a preinstalled SD card image[4]. The Pi 5 and Pi 4B run GNOME on Wayland with reasonable performance on 4GB+ models.
ARM64 goes first-class
Starting with 26.04, ARM64 packages have moved from ports.ubuntu.com to the main archive.ubuntu.com. This means proper mirror distribution, faster downloads, and the same infrastructure treatment as x86_64[9]. ARM64 is no longer a "ports" architecture.
Livepatch for ARM64
On June 23, 2026, Canonical announced live kernel patching for ARM64 servers[3]. This is the first time any major Linux distribution has offered rebootless kernel security fixes on ARM. The technical prerequisites -- upstream stack trace checks, the ARM64 consistency model, and the toolchain for producing loadable cumulative kernel modules on ARM -- took over two years to land.
For Raspberry Pi users running Ubuntu Server on Pi 4/5 in production (home servers, edge nodes, IoT gateways), this means critical kernel CVEs can be patched without downtime.
Ubuntu on WSL
The WSL story in 2026 is dominated by one announcement: WSL Containers hit general availability on September 29, 2026[10].
WSL Containers (WSLC)
Microsoft shipped wslc.exe -- a built-in CLI for building, running, and managing Linux containers directly on Windows, without Docker Desktop. Key capabilities:
| Command | Purpose |
|---|---|
wslc run | Run a container from an image |
wslc build | Build a container image |
wslc container cp | Copy files in/out via tar |
wslc system info | Environment state at a glance |
wslc network connect/disconnect | Attach/detach containers from networks |
wslc events | Stream real-time container activity |
container.exe | Built-in alias for familiar syntax |
There's also a WSL Containers API (NuGet package Microsoft.WSL.Containers) for running Linux containers programmatically from native Windows apps -- C# and C++/WinRT[10].
Enterprise controls ship on day one: Microsoft Intune can enable/disable the container feature and restrict image pulls to approved registries. Microsoft Defender for Endpoint extends its coverage to container workloads inside WSL[10].
Architecture
WSLC runs containers in a separate lightweight VM from your WSL distros. Each session gets its own wslcsession.exe process and storage VHD. File mounts use virtiofs for high-performance host/guest I/O. Networking uses a dedicated virtual switch with port mapping to the host[11].
WSL 3.0
WSL itself hit version 3.0 in late 2026, with automatic virtual NUMA support for large servers (fixing launch failures on machines with 256+ threads) and experimental sparse VHD creation that only consumes disk space for data actually written[12].
Ubuntu Pro on WSL
Ubuntu 26.04 on WSL integrates cloud-init and Ubuntu Pro, meaning enterprise users can attach their WSL instances to their Pro subscription for ESM security updates, FIPS compliance, and Livepatch -- the same coverage as bare-metal and cloud instances[4].
What this means
Three threads run through all of 2026's Ubuntu releases:
- Memory safety is no longer optional. Rust coreutils, sudo-rs, a Rust-native system monitor, and Rust as a permanent kernel language -- Canonical is systematically replacing C in security-critical paths. The GNU originals are still there, but the defaults have shifted.
- ARM64 is a first-class citizen. Archive migration, Livepatch, desktop ISOs, Pi 5 support -- the infrastructure gap between x86_64 and ARM64 is effectively closed.
- Containers everywhere. LXD on the server, WSLC on the desktop, Intune/Defender in the enterprise. The container is becoming the default deployment unit regardless of where Ubuntu runs.
For anyone choosing a Linux distribution for the next five years of production workloads, Ubuntu 26.04 LTS makes a compelling case. The security floor is materially higher, the hardware coverage is broader, and the tooling -- from kernel to container to IDE -- is more coherent than any previous release.
sudo apt update && sudo apt full-upgradeOr on a fresh install:
https://ubuntu.com/downloadFootnotes
- ↑ Canonical, "Ubuntu 26.04 LTS Release Notes", documentation.ubuntu.com, April 2026
- ↑ Ubuntu Release Team, "Ubuntu 26.04 LTS — changes since 25.10", documentation.ubuntu.com, April 2026
- ↑ Canonical, "Canonical announces live kernel patching for Arm64", June 23, 2026
- ↑ Canonical, "Canonical releases Ubuntu 26.04 LTS Resolute Raccoon", April 23, 2026
- ↑ Canonical, "What’s new in security for Ubuntu 26.04 LTS?", April 2026
- ↑ Serverspace, "Ubuntu 26.04 LTS Resolute Raccoon: A Complete Guide to What’s New", March 2026
- ↑ Canonical, "Ubuntu’s virtualization hardware enablement (HWE) stack: a new model for confidential computing enablement", 2026; server docs
- ↑ Ubuntu Release Team, "Ubuntu 25.04 Release Notes", documentation.ubuntu.com, April 2025
- ↑ Ravi (Ubuntu Architectures Team), "Ubuntu on ARM: summer ’26 update", discourse.ubuntu.com, June 2026
- ↑ L. Iyer, "WSL containers now generally available", Windows Developer Blog, September 29, 2026
- ↑ P. Boulay, "WSLC Architecture deep dive", Windows Command Line blog, September 29, 2026
- ↑ M. Larabel, "Windows Subsystem For Linux Can Now Run On Very Large Servers, Experimental Sparse VHD", Phoronix, October 2026